
Technology
CVE-2026-80521 container escape: check your Docker and k3s hosts and mitigate it
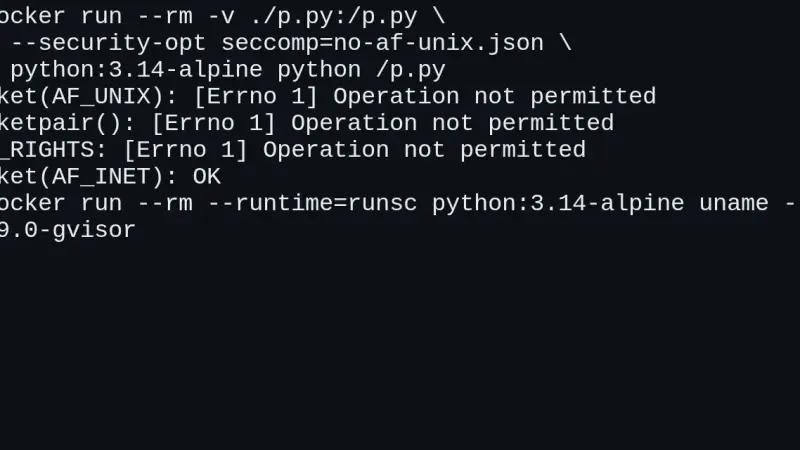
CVE-2026-80521 is a use-after-free in the Linux kernel's AF_UNIX socket garbage collector, with a public container escape exploit since 22 September 2026. You are affected if your kernel is 6.10 or later without the fix, or a 6.1 or 6.6 branch that received the backport. Patch and reboot; until then, isolate untrusted workloads with gVisor.
