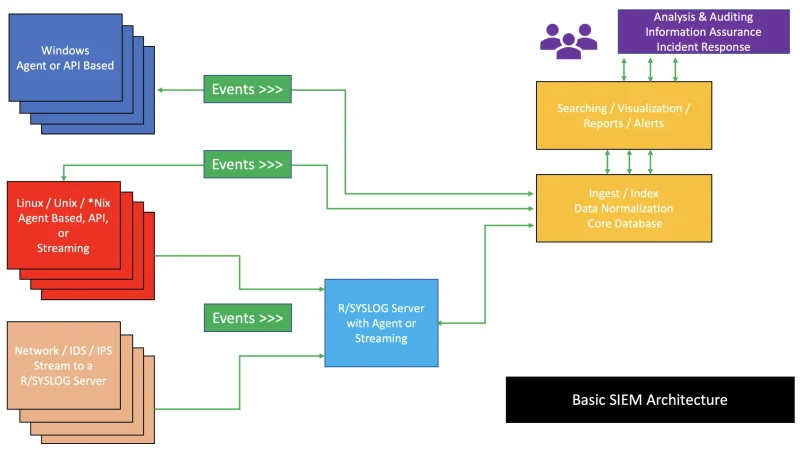
Two years after Zero Trust stopped being a marketing word, it is worth looking at how it connects with the SIEM teams run day to day. A look at useful signals, avoidable noise, and the decisions that actually change security posture.
Zero Trust is not a product but a security architecture. It discards the assumption that the internal network is trusted and verifies every access explicitly, with least privilege, assuming breach is already active. The five principles: verify explicitly, least privilege, assume compromise, validate the device, and continuous visibility.
Vault centralises secrets with automatic rotation, a full audit trail and granular access policies. A practical guide for teams moving beyond a .env file: the concepts you actually need, the setup that works, and the mistakes that make the migration painful.
6 min2624.4
We use first- and third-party cookies to analyze site traffic. You can accept them, reject them, or configure your choice.
Learn more about cookies
Cookie preferences
NecessaryEssential for the site to work. Always on.
AnalyticsHelp us understand how the site is used (Google Analytics).